
THANK YOU FOR SUBSCRIBING
× 
Enterprise Security Mag Weekly Brief
Be first to read the latest tech news, Industry Leader's Insights, and CIO interviews of medium and large enterprises exclusively from Enterprise Security Mag
Enterprise Security Magazine: Specials Magazine
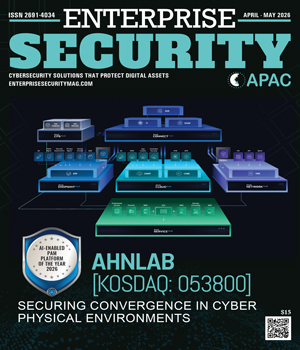
Cybersecurity is being reshaped by the convergence of IT and operational systems as environments that were once separate now operate as interconnected structures. Threats no longer remain confined to isolated endpoints and instead move across industrial control systems, enterprise networks and edge devices that share common architectures. As this interconnection increases exposure, protection depends on maintaining visibility, control and response across systems that were historically segmented. In this setting, security execution becomes a system-level function where resilience is defined through alignment across digital and physical operations. As convergence continues to reshape how systems interact, organizations are rethinking how security is structured, moving away from fragmented tools toward integrated models that operate across environments. The challenge extends beyond detection to maintaining continuity in systems that cannot afford disruption. AhnLab, a cybersecurity provider delivering protection across endpoints, networks and operational systems, addresses this need through an integrated architecture that enables consistent visibility, coordinated response and reliable control across distributed and interconnected environments. Coordinated Protection across IT and OT Layers Protection across converged environments begins with coordination rather than isolated defense mechanisms. AhnLab structures its capabilities so that endpoint, network and operational layers function as interconnected components within a broader security system. Endpoint protection identifies malware, ransomware and abnormal behavior at early stages, generating signals that indicate potential compromise. These signals are not treated independently but contribute to a wider monitoring framework that tracks activity across environments, allowing security teams to understand how threats develop and move within systems. Network visibility strengthens this foundation through continuous monitoring of traffic patterns and communication flows. Suspicious activity, including lateral movement, can be identified in relation to endpoint signals, creating a more complete view of system behavior. Centralized management enables real-time observation of these interactions, reducing delays between detection and response while improving accuracy in threat assessment. The ability to correlate activity across layers ensures that response actions address root causes rather than isolated symptoms. Threat intelligence reinforces coordination by continuously updating detection models based on emerging attack patterns. Intelligence is integrated into the system so that protection evolves alongside threat landscapes without requiring manual intervention. As new vulnerabilities or techniques are identified, security controls adjust accordingly, maintaining alignment with current risks. This dynamic adaptation supports consistent protection while preserving operational stability across environments that require uninterrupted performance.
Digital Magazine
Digital Identity Verification of the Year in Asia 2026
Why has digital identity become foundational to enterprise security today? The Asia-Pacific region today stands at the intersection of two formidable forces. On one side, digital economies are expanding fast, reshaping how citizens access financial services, and everyday digital interactions. On the other, cyber threats are escalating in both frequency and sophistication, imposing immense pressure on enterprises and governments to secure trust. In this environment, identity verification has moved from a back-office compliance function to a foundational pillar of enterprise security. It is within this context that Thailand’s National Digital ID Company (NDID) has emerged as a benchmark, earning recognition as the Digital Identity Verification of the Year in APAC 2026 by Enterprise Security Magazine APAC. Founded in 2018 and headquartered in Bangkok, NDID operates as a consent-driven, federated digital identity network where both public and private-sector institutions can function seamlessly even as they retain full responsibility for their customers and data. That too under their own regulatory frameworks. While NDID itself takes up the painstaking job of governance, rule adherence and trust orchestration. “NDID was designed as a consent-driven, federated network because we believed this was the only model that could work sustainably at national scale,” “Digital identity is not a product; it is national infrastructure. Our role is to make trust interoperable across industries, while preserving institutional accountability and user consent.” says Boonsun Prasitsumrit, CEO. In practice, NDID ensures that trust, privacy, and interoperability move together. Personal data within the network is never centralized. It remains securely with the original data owners and is exchanged only when users provide explicit, purpose-based consent. While, Interoperability is achieved through common standards and processes, rather than forcing all participants into a single system or technology stack. When these elements are aligned, consent becomes practical, allowing users to authorize transactions with confidence and institutions to rely on verified outcomes. High-Trust Transactions minus the Physical Presence How does NDID enable secure cross-institution identity transactions across Thailand’s digital economy? The tangible value of this model is most evident in high-trust transactions that traditionally required physical presence. One of the clearest examples is cross-bank digital account opening. Historically, even customers with an established relationship at one bank were required to visit a branch in person to open an account with another institution. This process involved duplicate know-your-customer checks, extensive paperwork, and significant time and operational cost..
Security Authentication Solution
Cyber threats lurk around every digital corner, pushing businesses to protect their data with fortress-like security while fostering growth and customer trust. Rising to meet this challenge is Soft Giken, a forward-thinking Japanese company empowering organizations with robust security infrastructures. Central to its offering is YubiOn, a cloud-based advanced authentication solution designed to strengthen endpoint security by leveraging technologies like advanced multifactor authentication (MFA), FIDO2 and enterprise attestation. Traditional ID and password methods fail to protect businesses from phishing attacks or help them meet evolving regulatory demands. That is prompting many organizations to transition toward zero-trust architectures. Yet, adopting these advanced security models often comes with high implementation costs and integration challenges— particularly for businesses with legacy systems that struggle to support modern authentication methods. Seamless Integration And Custom Security Solutions YubiOn addresses these challenges by providing tailored, cost-effective solutions that seamlessly integrate into existing systems. With devices like YubiKey and other security key solutions, YubiOn delivers robust MFA while harnessing FIDO2 standards for biometric and passkey-based authentication. “We enable businesses to implement top-tier security without disrupting workflows, effortlessly enhancing protection and user experience while delivering globally accessible security solutions,” says Norio Fujita, founder. Soft Giken introduced the first passkey-based PC login, eliminating traditional passwords and enhancing security and user convenience. The shift toward passwordless authentication with YubiOn is a game-changer. It boosts employee productivity by preventing account lockouts and reduces IT-related burdens. The solution also supports secure remote access, essential for organizations embracing flexible work models. YubiOn fosters digital transformation by balancing innovation with high-level security. From Standalone To Comprehensive Cloud-Based Security Originally launched as YubiOn Windows Standalone, the solution provided OTP authentication using YubiKey. Over time, YubiOn’s capabilities were expanded, supporting Mac environments and biometric authentication with AT.Key.
Information Security Solutions
A subtle yet significant shift is unfolding in Tokyo. Since 2014, a team of security engineers and innovators at ZenmuTech (TYO: 338A) has been rethinking what data protection should look like in an age where cyberattacks are a daily reality and traditional encryption often feels like putting a padlock on a glass door. The idea behind their solution is surprisingly straightforward. Instead of trying to make data harder to steal, ZenmuTech makes it pointless to steal in the first place. It does not rely on tougher encryption or more complex keys. Instead, it splits data into meaningless fragments before leaving a device. Unless all those fragments are brought back together, there is nothing to read, decrypt, or leak. At first glance, that concept seems almost too simple. But it is precisely what modern security needs. Making Data Meaningless Until You Need It ZenmuTech’s approach is different from the conventional wisdom in cybersecurity. Most solutions still revolve around who can access data, with layers of firewalls, keys, and permissions. However, access controls alone are insufficient in a world filled with insider threats, remote work, and distributed cloud systems. The company’s core technology is built on secret sharing, using an All-Or-Nothing Transform (AONT). Rather than encrypting and storing files in a single location, ZenmuTech splits data into fragments. These fragments are completely useless on their own. Only when all fragments are reassembled can the original data be reconstructed. Without that, the information remains an empty shell. This approach stands out because it eliminates the need for encryption keys. In most security breaches, attackers are after the keys or the backdoors. By removing keys from the equation entirely, ZenmuTech eliminates one of the most vulnerable pressure points in data security. This is especially effective in zero-trust environments where it is assumed that every user, device, and network segment could be compromised. With ZenmuTech’s system, there is simply no single point of failure. No matter how sophisticated the attacker, unless they get everything, they get nothing. Practical Security That Works In The Real World Security, however, is not just about protecting data. It is also about keeping people productive. That is where ZenmuTech earns its reputation. Its solutions are designed to be used by real teams in real businesses, not just security professionals. The company has earned praise for its easy interface, fast performance, and the fact that it does not get in the way of daily work.
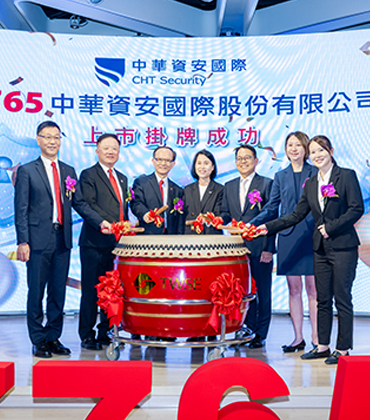
How are enterprises balancing AI adoption with the need to secure AI-driven environments?
CHT Security has framed its direction around a two-sided reality now shaping enterprise risk: empowering cybersecurity with AI and safeguarding AI with cybersecurity.
AI is moving deeper into enterprise operations and security teams now protect more than networks, endpoints and cloud infrastructure. They must also secure AI applications themselves, where model behavior, data exposure, misconfiguration and misuse create risks that traditional controls were not built to address.
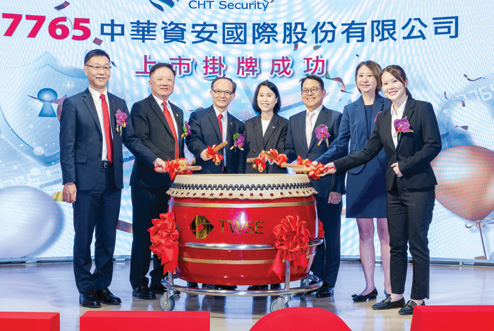 CHT Security delivers dedicated protections for enterprise AI environments through AI Application Security Testing and AI Security Diagnostics, alongside AI-enabled SOC services. These services cover security validation, diagnostics, continuous protection, monitoring and incident response for AI applications in active business deployment.
The work is no longer theoretical. CHT Security has deployed these services for financial institutions and high-tech companies, building operational experience in environments where AI adoption must be matched by security discipline from the start.
That direction extends from a broader SOC model built around monitoring across diverse client environments. Decision quality under pressure requires more than prompt alerts. It requires context, traceability and a shared understanding of how attacks unfold.
How does contextual threat intelligence improve detection accuracy and response quality?
The SOC operates within an ISP environment through its parent company, Chunghwa Telecom, giving it access to cross-border threat intelligence on malware activity and attack patterns. Carrier-grade visibility enables earlier threat identification and gives analysts more context when investigating suspicious behavior. Signals feed forensic and reverse-engineering work as patterns begin to form. Analysts can act earlier, before incidents escalate.
Analysts move findings into retrospective analysis, tracing related activity within retained logs and monitored environments, subject to customer telemetry and retention policies. They reintegrate newly confirmed indicators and refined detection logic into SOC monitoring workflows, shortening time to recognition when similar tactics reappear.
To maintain consistent analysis under load, the SOC maps all activity to the MITRE ATT&CK framework, tying each event to known adversary tactics and techniques. Analysts across shifts assess incidents using the same reference points, cutting interpretation variance.
CXO INSIGHTS
The Evolution of Vulnerability Management: Rise of the Attack Surface
Joel Earnshaw, Senior Manager Cyber Security, Perenti
The Shift from Cybersecurity to Product Security: A Business Imperative
Peter Wong, Head of Information Security and Compliance, APAC, Edenred
7 Maxims From Sun Tzus The Art Of War For Modern Cyber Threat Intelligence
Frankie Shuai, APAC CISO, DWS Group
Mastering the Complexities of Modern Cybersecurity
Wouter Veugelen, Senior Managing Director & Head of Cybersecurity, Australia, FTI Consulting
Leading Ethical Digital Transformation in Islamic Finance
Yusni Yunus, Deputy Vice President, Embeded Risk and Compliance, Group Chief Operation Officer, Bank
IN FOCUS
EDITORIAL
Establishing Trust in a Digital-First Economy
The Asia-Pacific region stands at the intersection of explosive digital growth and intensifying cyber-threats. As digital economies rapidly expand, identity verification has evolved from a mere compliance function into a foundational pillar of enterprise security. This edition of Enterprise Security Magazine APAC examines digital identity verification as a key driver of secure innovation and economic growth.
Our cover story features AhnLab, a leading cybersecurity provider offering integrated protection for converged IT and OT environments. Through endpoint security, network visibility, and coordinated threat response on a unified platform, AhnLab delivers consistent defense, minimal disruption, and operational resilience across industrial and enterprise systems.
National Digital ID Co., Ltd. (NDID), honored as the Digital Identity Verification of the Year in Asia 2026, operates a consent-driven, federated digital identity network without a central authority. Founded in 2018 and headquartered in Bangkok, Thailand, NDID supports over 60 million usable digital identities, more than 30 million registered accounts, and approximately 2 million monthly transactions across over 180 member organizations, including major banks, telecoms, government agencies, and regulators. It enables high-trust, privacy-first transactions such as cross-bank account opening, lending, securities services, e-tax filing, and public services, powering Thailand’s digital economy.
Contributors extend these themes. Ho Chee Keong, Senior Vice President - Architecture, Cybersecurity, Infrastructure at MSIG Asia frames Zero Trust as an enterprise-wide resilience strategy requiring identity and device verification, breach containment and vigilance toward trusted partners. Frankie Shuai, APAC CISO at DWS Group, applies Sun Tzu’s seven maxims to cyber threat intelligence: knowing adversaries and assets, proactive prevention, rapid response, collaborative sharing, risk-prioritized allocation, defensive deception and continuous adaptation.
Together, these insights highlight that excellence in digital identity rests on verified trust, strong governance, and proactive intelligence.
